





AI governance is a DLP problem
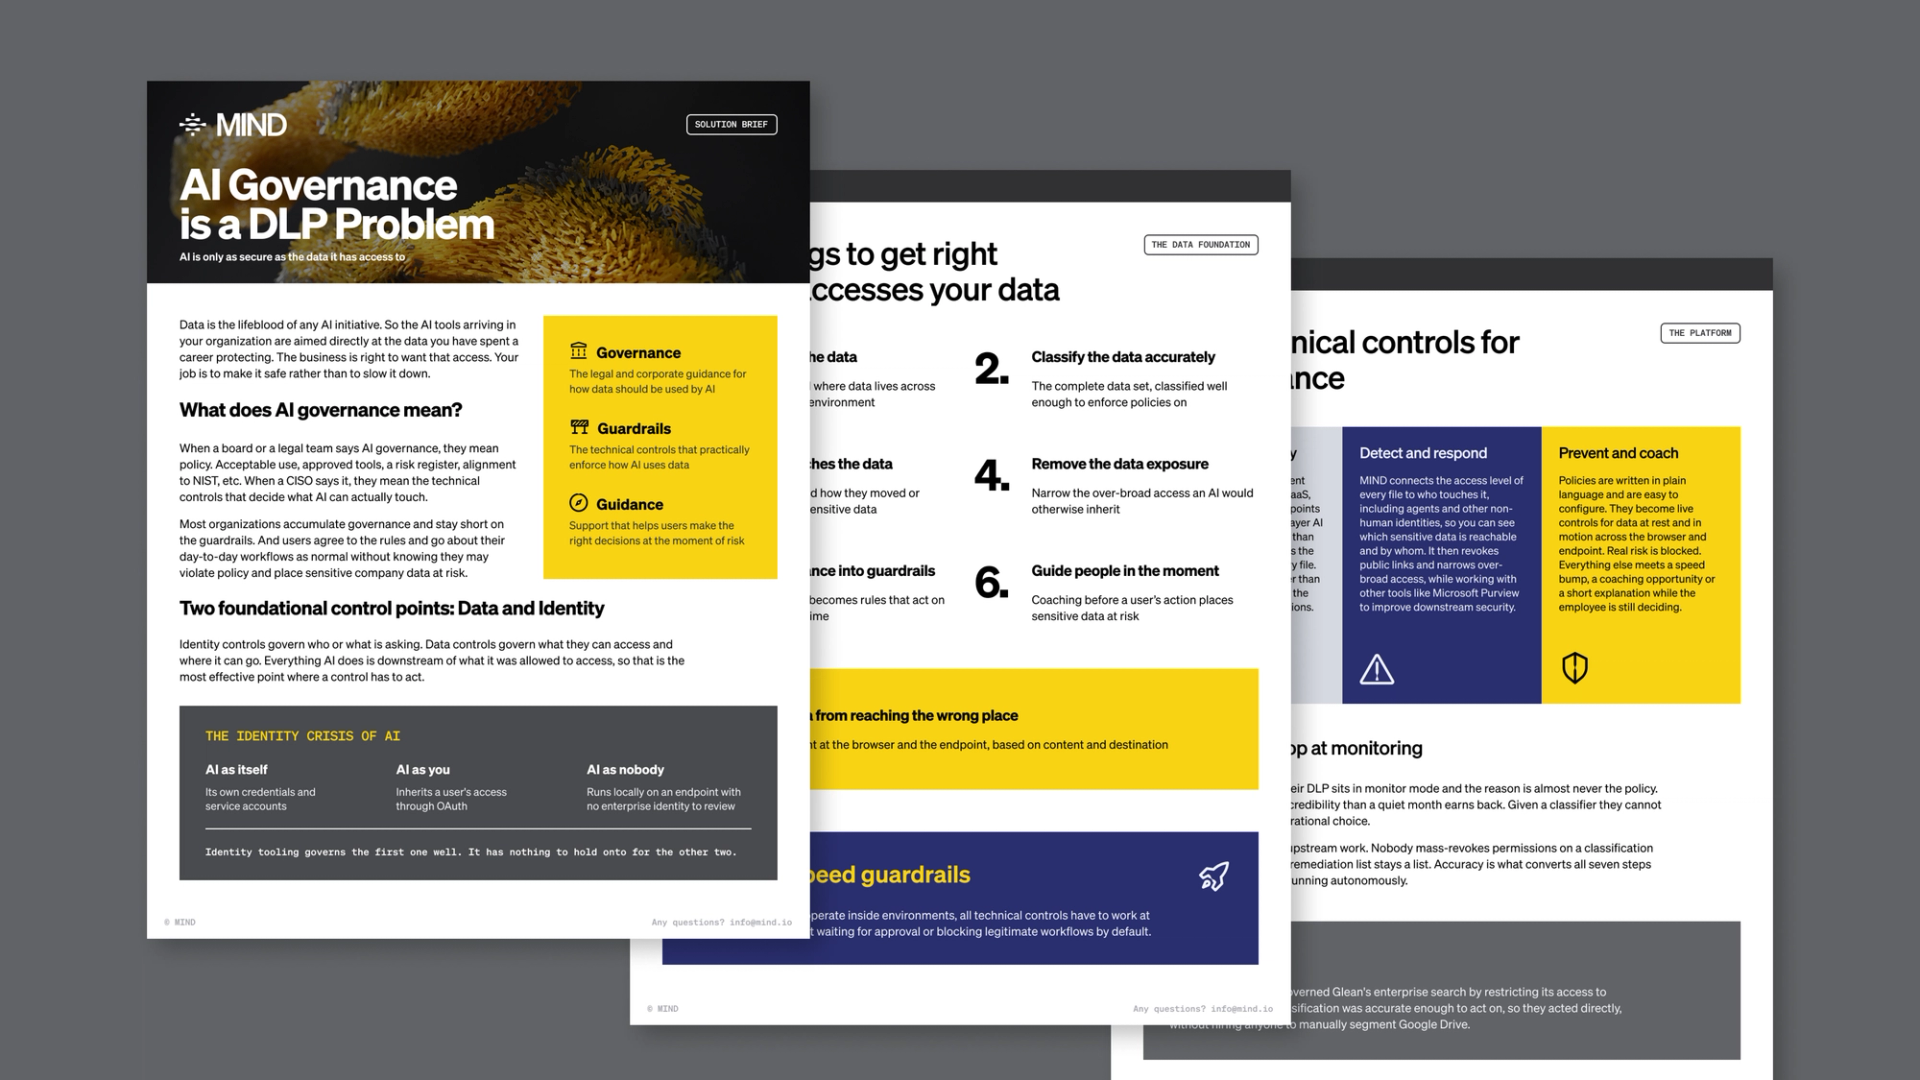
AI governance usually starts with policy: acceptable use rules, approved tools and a risk register. But AI is only as secure as the data it can reach, and policy alone can't stop a GenAI tool or an AI agent from touching files it shouldn't. That's why AI governance is really a data loss prevention (DLP) problem.
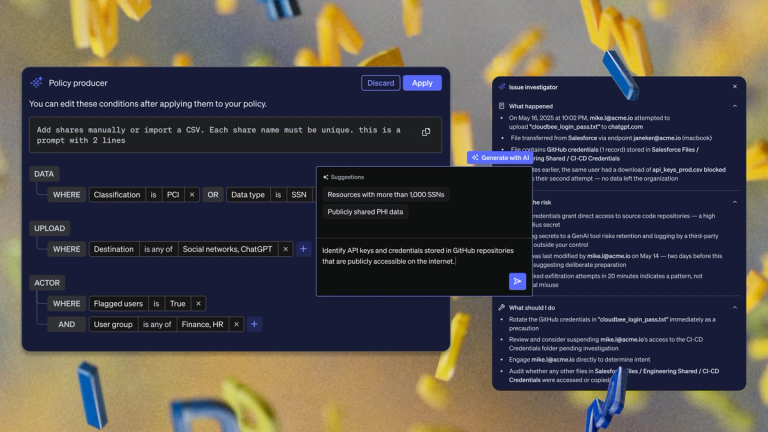
Identity controls tell you who or what is asking. They can't govern AI that inherits a user's access through OAuth or runs locally on an endpoint. Data controls can. When you know where sensitive data lives, how it's classified and who can reach it, you can turn governance into guardrails that act in real time.
This solution brief lays out seven things to get right before AI accesses your data, from discovery and classification to enforcement at the browser and endpoint. It also shows how MIND helps security teams say yes to AI adoption without putting sensitive data at risk.
See for yourself how MIND can help you secure the data that AI uses in your environment.